Overview
Toobit engaged Hacken to run penetration tests of its web application, API, and native Android and iOS apps. The engagement followed Toobit's earlier ISO/IEC 27001:2022 certification with Hacken.
About Toobit
Toobit is a centralised cryptocurrency exchange, launched in 2022 and licensed as an Money Service Business (MSB) under FinCEN, serving users in more than 100 countries.
Audit Approach
Hacken ran three black-box penetration tests covering Toobit's web application and API, Android app, and iOS app. Each test assessed authentication, session management, authorisation, and relevant storage and platform-hardening controls. The penetration tests followed Hacken's methodology, aligned with NIST SP 800-115, PTES, and the OWASP Testing Guide.
Key Findings
The most significant findings concerned object-level authorisation on Toobit's social Insights feature. Several endpoints allowed an authenticated user to access another user's private insight and its associated comments or interactions, regardless of the owner's privacy settings. The issue could be triggered through direct requests and actions such as reposting, commenting, translation, and liking. Toobit fixed these issues by enforcing ownership and privacy checks server-side rather than relying on client-side controls.
Both mobile apps stored session tokens and cookies in cleartext in local storage (SharedPreferences on Android, NSUserDefaults on iOS), and the iOS app disabled App Transport Security globally. The token-storage issues were fixed. Other platform-hardening findings, including the lack of jailbreak detection and screenshot protection, were accepted as lower-priority risks.
On the web platform, a support-ticket endpoint for reporting deposit issues lacked rate limiting, letting an account flood the queue with duplicate tickets, and a state-changing action lacked CSRF protection, allowing an attacker to stop a victim's active trading bot from an external page. The rate-limiting issue was fixed; the CSRF finding, along with account-enumeration and password-reuse findings on lower-sensitivity settings, was accepted.
Audit Results
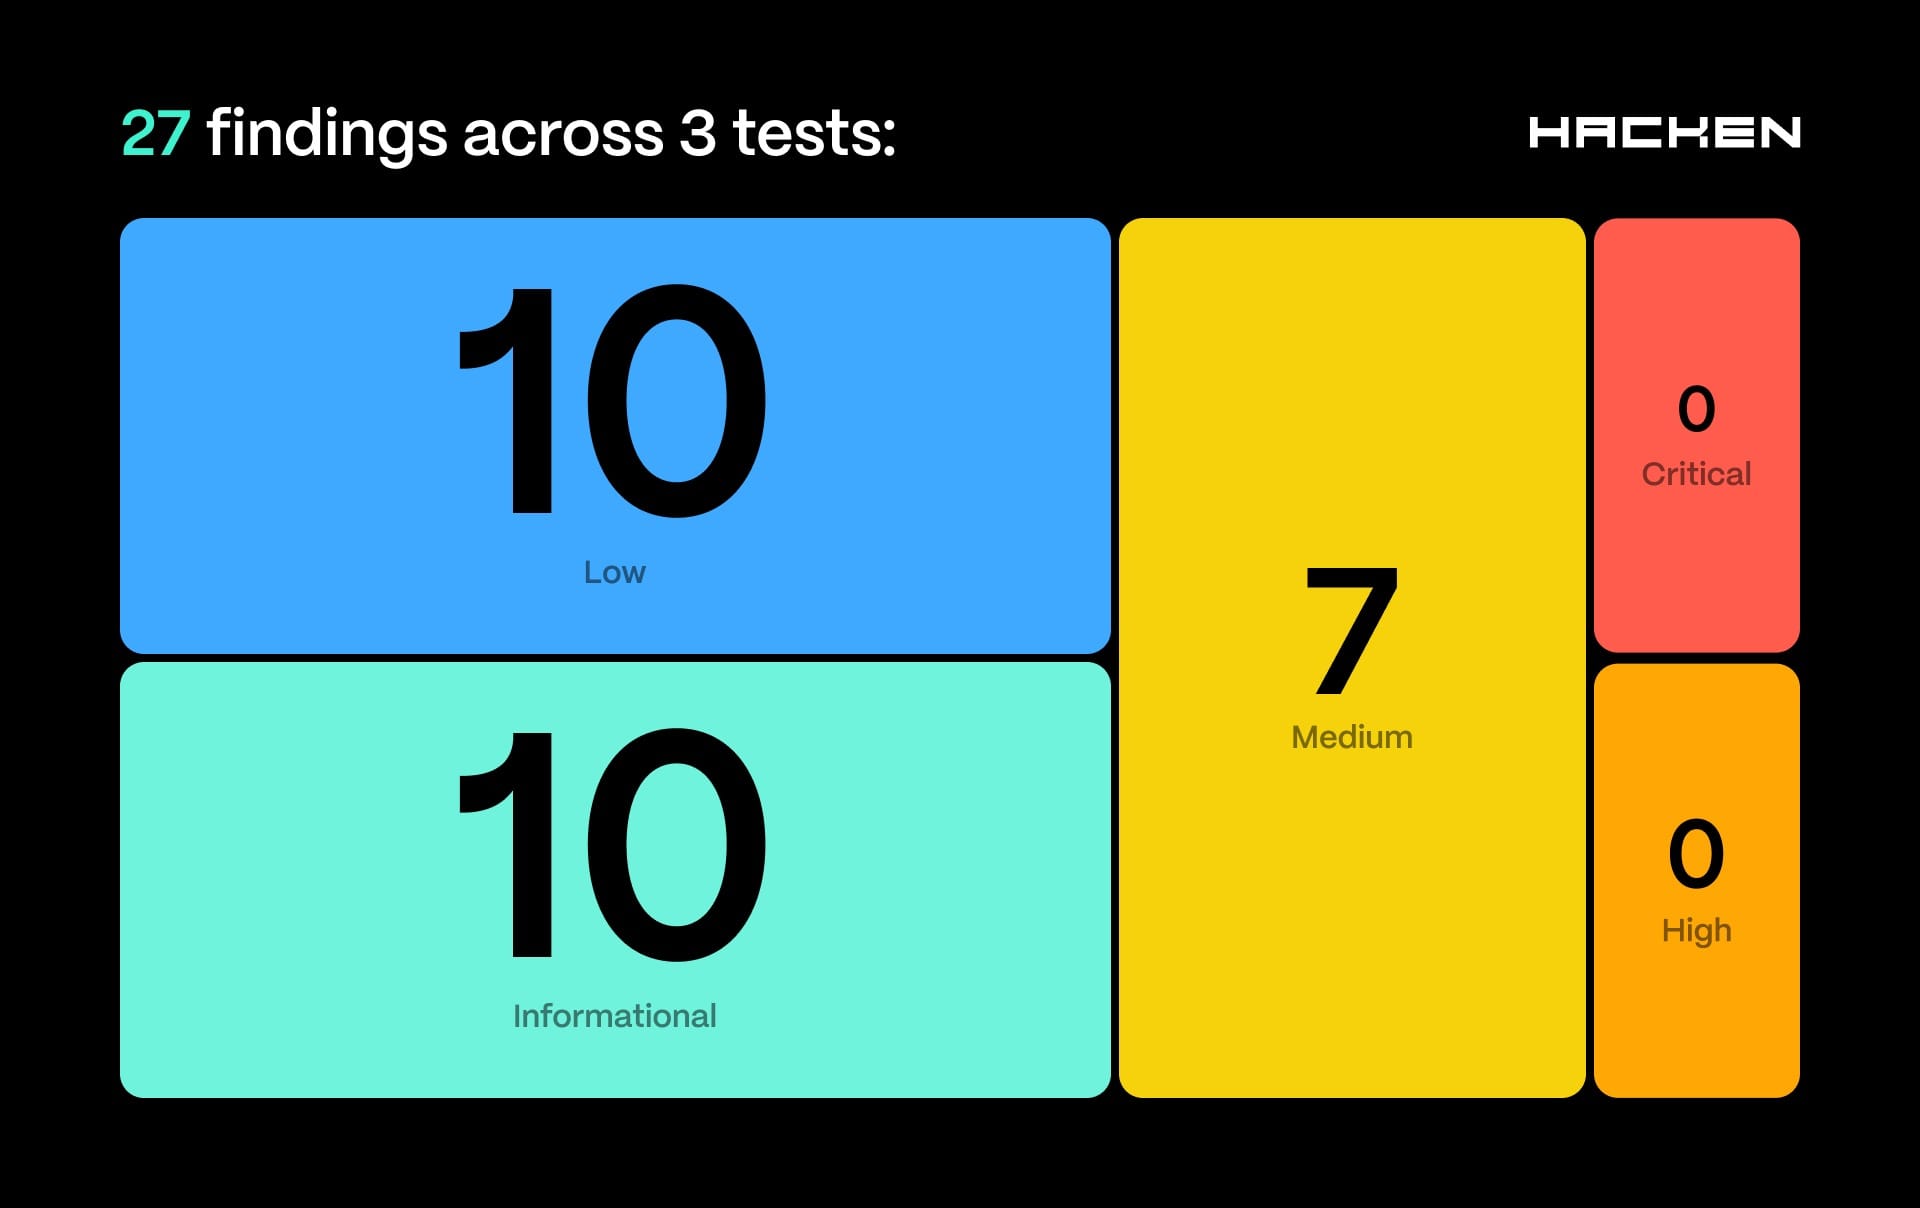
The three penetration tests recorded 27 findings:
Of the 27 findings, 9 were resolved and 18 were accepted by Toobit. All 7 Medium-severity findings were fixed. Two Informational findings were also resolved: a 2FA bypass affecting anti-phishing code changes and an authorisation gap on private-insight replies. Other low to information findings were accepted by Toobit.
Key changes delivered:
- Server-side authorisation added across insight, comment, reply, repost, like, and translation endpoints on the Insights feature.
- Session tokens and cookies moved out of cleartext local storage on Android and iOS.
- Rate limiting added to deposit-ticket creation to stop mass-ticket abuse.
- Step-up 2FA verification required before anti-phishing code changes.
Read the full reports: Web & API, Android, and iOS.
Request a Penetration Test
Hacken provides penetration testing for applications, financial institutions, centralised exchanges, wallets, and trading platforms across Web2 and Web3 environments.
Each engagement combines automated analysis, manual security review, and proof-of-concept validation, performed by Hacken's in-house security team.