Hacken conducted a security review of CollaFi, a peer-to-peer NFT lending platform built natively on Hedera. The engagement assessed the application’s backend and the systems supporting NFT-collateralised lending, including its integration with Hedera Token Service (HTS) and Hedera Consensus Service (HCS).
About CollaFi
CollaFi enables NFT holders to access HBAR liquidity without selling their assets. Borrowers use NFTs as collateral, while lenders fund individual loan offers and earn interest on completed loans.
The platform is built around Hedera-native infrastructure, using HTS for asset and HBAR transfers and HCS for transaction processing. Because CollaFi does not rely on smart contracts for its transaction logic, the security model differs from conventional EVM-based lending applications.
Because CollaFi uses Hedera Consensus Service rather than smart contracts to coordinate its transaction architecture, transactions are not exposed to the same front-running mechanism based on observing and reordering pending transactions in a public mempool.
Audit Approach
Hacken reviewed CollaFi’s backend application and its interactions with the underlying Hedera infrastructure. The assessment covered the main components supporting lending operations, asset handling, authentication, administration, rewards, and transaction processing.
Hacken combined code review and security testing to identify vulnerabilities across the application and provide actionable findings for remediation.
The audit covered the systems that support CollaFi’s core platform operations, including:
- Lending and loan management
- NFT and HBAR handling
- HCS-based transaction processing and settlement
- Authentication and authorisation
- Administrative functions
- Rewards and quests
- External service integrations
- Internal transaction and settlement processes
Audit Results
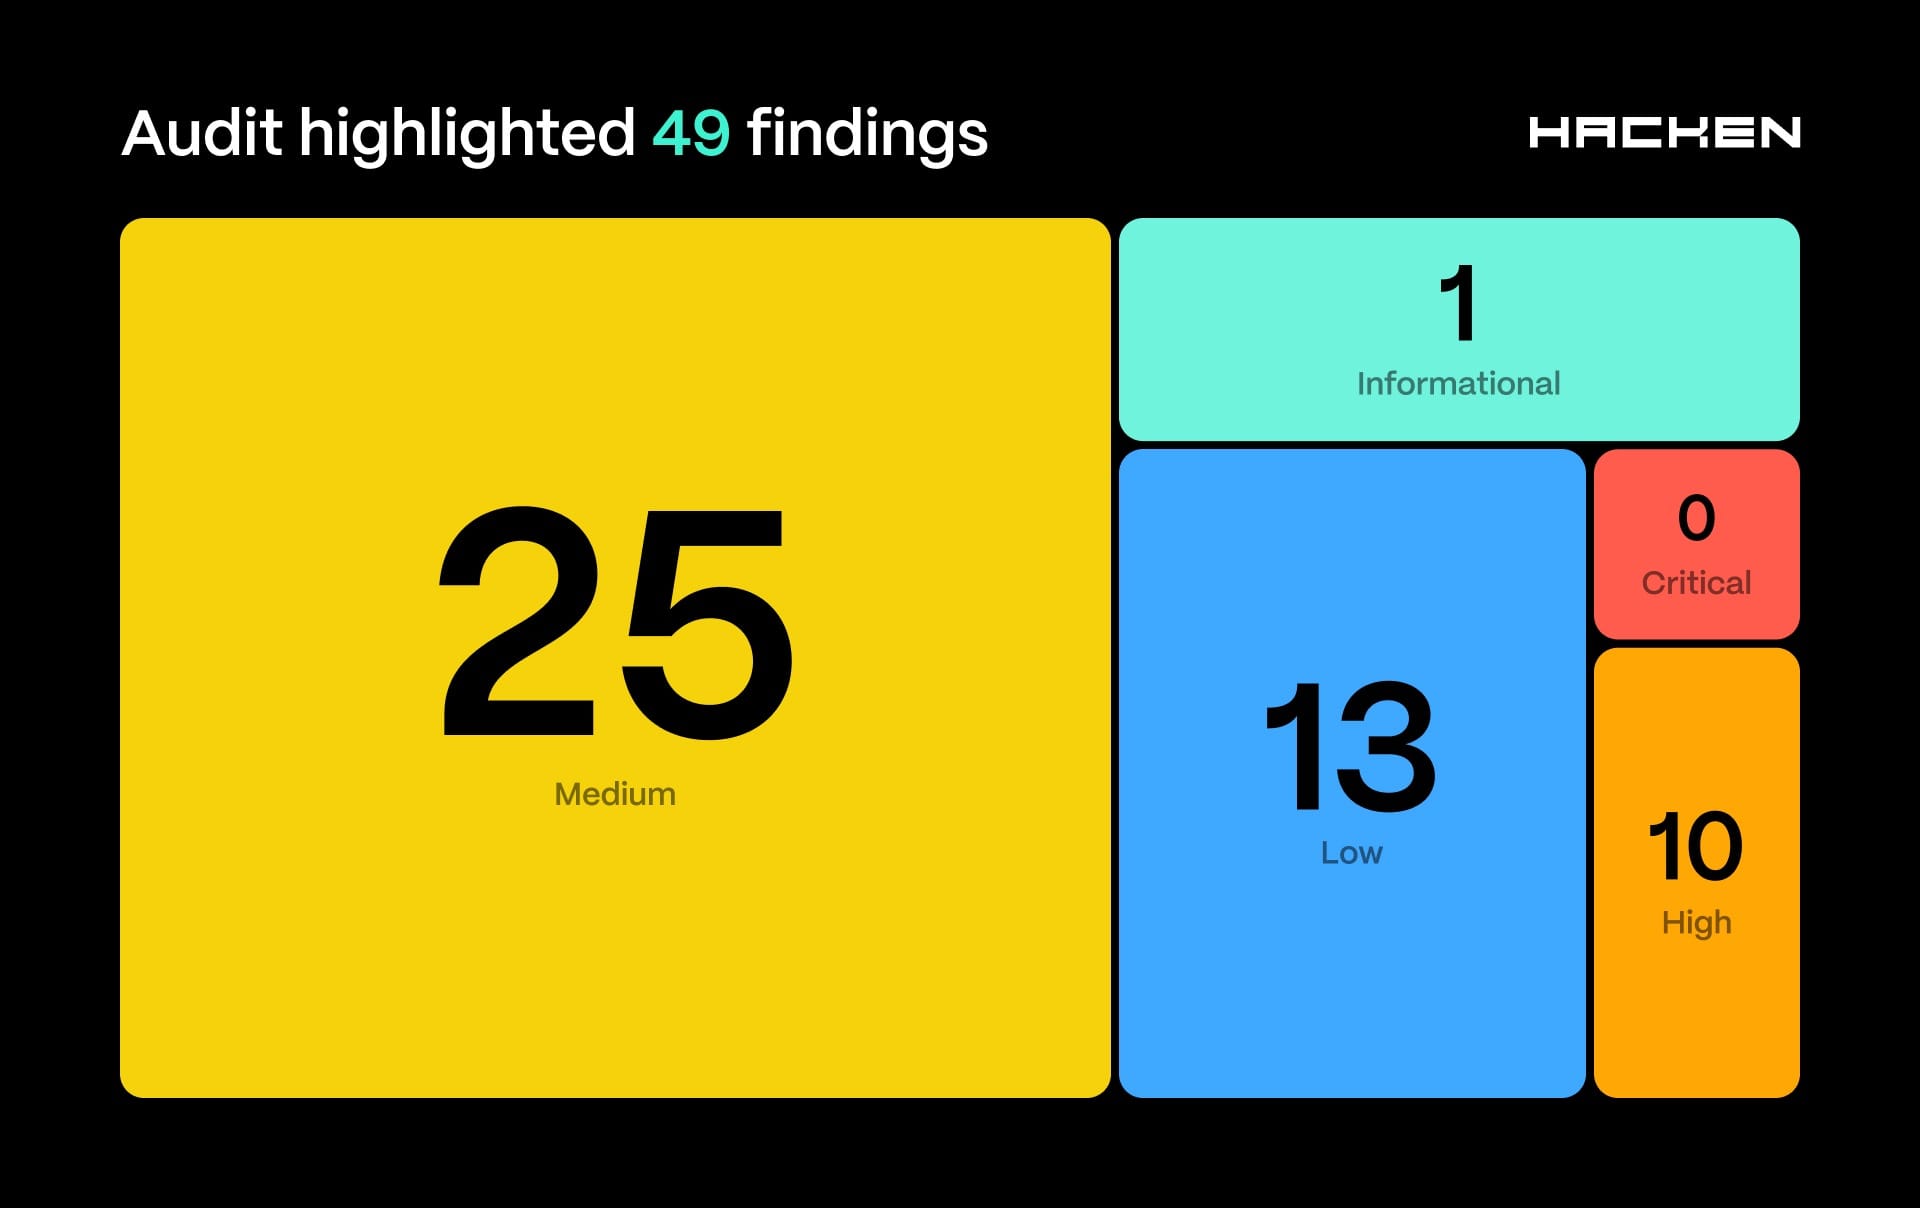
The assessment identified 49 findings across CollaFi’s application and supporting infrastructure. The number reflects the scope of the review, which covered the backend systems responsible for lending, asset handling, authentication, administration and transaction processing rather than a conventional smart contract audit.
CollaFi resolved 45 findings following the review, while four were accepted. The final status of each finding, together with the methodology, scope and technical details, is documented in the full audit report.
Read the Full CollaFi Security Audit Report: https://hacken.io/audits/collafi/dapp-collafi-source-code-review-jul2026/
The engagement also marked Hacken’s first audit of an HCS-native application, extending the review beyond conventional smart contract security to the systems connecting Hedera services with off-chain application logic.